

Howdy,
I have a url like this:
http://localhost/wconnect/about.awp?param=<br><%2ftitle>f<svg onload=alert("XSSTest")>
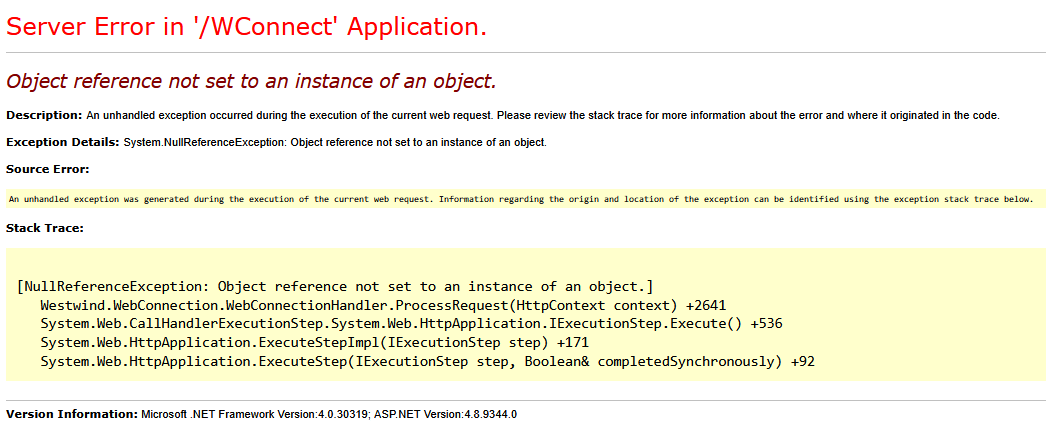
On localhost I'm getting this:
But on a production site I'm getting this:
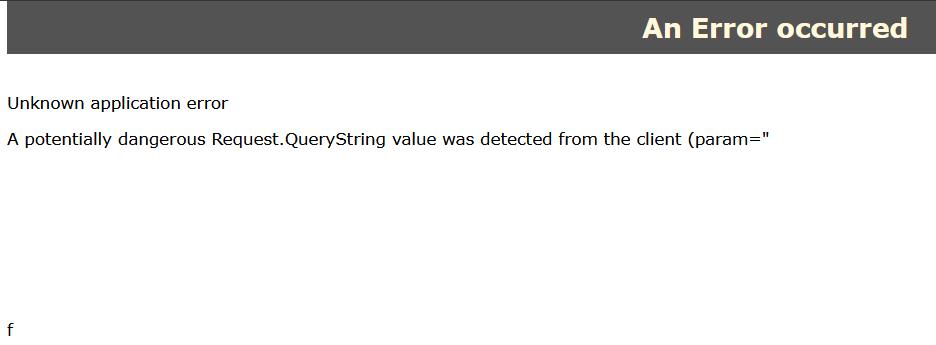
Which is rendering the BR tag in the url. So the alert is blocked but there's still some potential for bad stuff it seems.
This site isn't behind a WAF like the others, which seems to be where this should really be blocked.
But curious if you can tell me what's going on with my localhost, and maybe if this is something you've already addressed. (The site in question is on Web Connection .NET Handler 8.1.2)

Yeah that's an ASP.NET feature that looks for dangerous form and query string data and throws an exception. The difference between live and dev is likely the IIS error handling and reporting behaves differently in localhost vs. full site scenarios.
The live behavior is what I would expect - that's internal to the ASP.NET runtime and is correctly handled.
I took a look what happens in dev mode and what I see is that the ASP.NET request is served with a Null reference for HttpContext.Current which realistically should not happen. Effectively there's nothing that the code can do with that since without context I can't even write basic output or send an error response.
So, looks like there's nothing I can really do about this, but seeing that the deployed behavior is correct, that's probably not a problem.
+++ Rick ---